OpenSSF

Inaugural Open Source Security Singapore Meetup

We’re delighted to invite you to Singapore’s inaugural Open Source Security Foundation (OpenSSF) Meetup on the evening of Thursday, the 8th of June at the AWS Singapore Office to discuss how we can address cybersecurity challenges locally and globally.
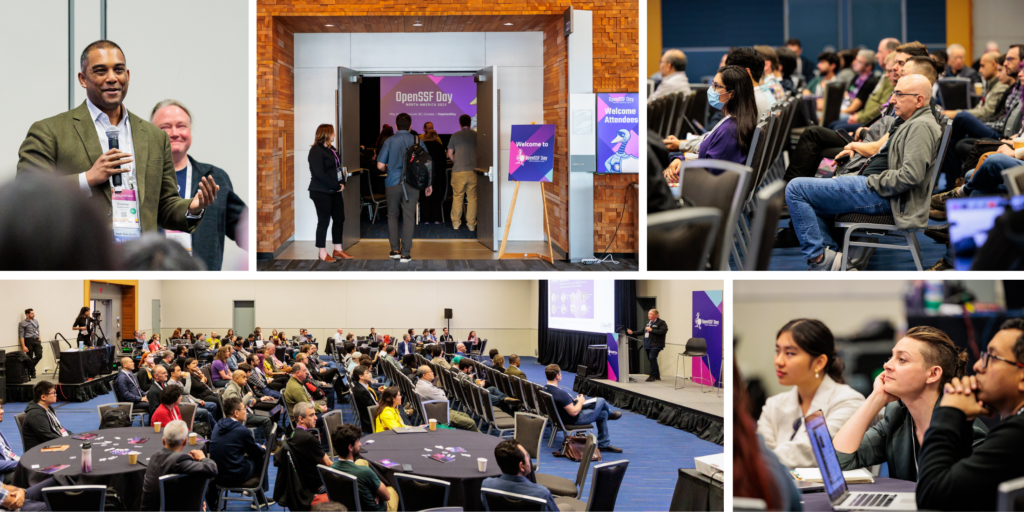
Takeaways from OpenSSF Day North America

We recently hosted OpenSSF Day at the Open Source Summit North America in Vancouver, BC with a full day of session presentations, panels, and lightning talks around the current state of open source security. If you weren’t able to attend, the videos are now available on our YouTube channel to view, and here are a…

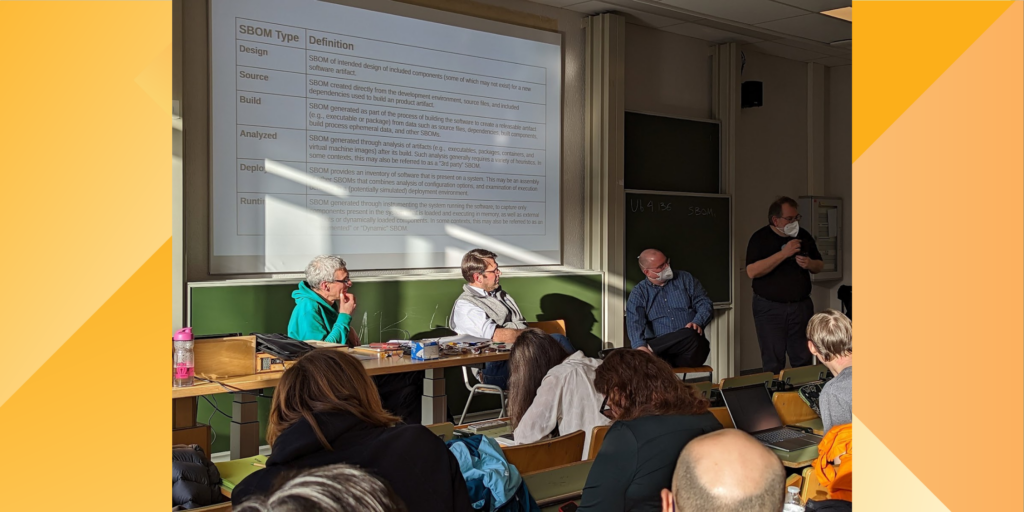
Exploring the Latest Advances in SBOMs from the Devroom

Where we are with SBOMs and where may the community go in the future? At the 2023 SBOM Devroom, hosted at FOSDEM 2023 in Brussels, participants discussed various topics related to generating, understanding, managing, and converting Software Bill of Materials (SBOMs).

How I Got Involved with the OpenSSF

Let’s get it out of the way early: it’s not always clear how you can best plug into organizations like OpenSSF. That’s why I’m writing this guest blog post as an “outsider.” I’m just your average tech employee who has become progressively more involved since my company, Sonatype, became members of OpenSSF. If you’re connecting…

OpenSSF Announces SLSA Version 1.0 Release

The Open Source Security Foundation (OpenSSF) is proud to announce the release of version 1.0 of Supply-chain Levels for Software Artifacts (SLSA). SLSA is an OpenSSF project that provides specifications for software supply chain security, established by community expert consensus. The stable release of the SLSA 1.0 Build Track lowers the barrier of entry for…

Assessing Product Risk Using SBOMs and OpenSSF Scorecard 

The use of SBOMs is becoming increasingly essential in managing software supply chains. The main consumption use case is for evaluating dependencies known-vulnerabilities risk, by mapping the dependencies listed in the SBOM to CVEs. In this blog post, we propose using SBOMs alongside OpenSSF Scorecard to evaluate a product's risk.

SBOMs, So Far, So Good, So What?

We’ve been discussing the creation of SBOMs for over ten years, but has it gotten us any closer to hardening our software development practices? SBOMs provide critical supply chain data, but we are simply not using the data to drive our supply chain decisions. Requiring SBOM generation alone is not the answer. What is the…