
The August 2026 OpenSSF Newsletter spotlights a wave of CRA readiness content, from a new Ericsson case study to a CRA podcast playlist. This issue also highlights new project announcements, releases, and working group updates. Learn more about securing agentic AI with OpenSSF at AGNTCon and MCPCon North America.
TL;DR:
- 🤖 Join OpenSSF at AGNTCon + MCPCon North America: Securing Agentic AI → Two sessions and a booth focused on securing agentic AI.
- 📘 Case Study: Ericsson Conquers the CRA with 1,400 Upstream Fixes → How shifting to upstream collaboration eliminated private forks and met CRA obligations.
- 🛠️ CRA Readiness: A Practitioner’s Guide to Compliance → A pragmatic path forward as the September 2026 reporting deadline nears.
- 🔐 Announcing BOMHort → Kubernetes-Native SBOM visualization and governance at scale
- 🎙️ Podcast: Four New Episodes → CRA deadlines with Dave Russo, community gardening the CRA with Roman Zhukov, practical CRA strategies with Megan Knight, and funding open source with AWS’s Mila Zhou.
- 📅 ENISA’s Single Reporting Platform guides updated ahead of the September 11 CRA reporting go-live.
5 min read
Happy 35th Birthday to Linux! 🐧🎉

(Image created with Gemini using prompt: “Image of the OpenSSF mascot, Honk, celebrating Linux’s birthday with Linux’s mascot, Tux”)
From a “just a hobby, won’t be big and professional” Usenet post by Linus Torvalds on August 25, 1991, to the powerhouse driving world-class servers, supercomputers, cloud infrastructure, and billions of mobile devices today, the kernel’s journey is unmatched.
Want to hear how the kernel stays secure after 35 years? Listen to What’s in the SOSS? Podcast (#64) where CRob sits down with Linux kernel maintainer and legend Greg Kroah-Hartman to discuss how a weekend driver project turned into 25+ years of kernel maintenance, why upstream bug fixes are the ultimate security strategy, and how OpenSSF collaborates to protect open source maintainers amid global regulations like the EU’s Cyber Resilience Act (CRA).
Join OpenSSF at AGNTCon + MCPCon North America: Securing Agentic AI
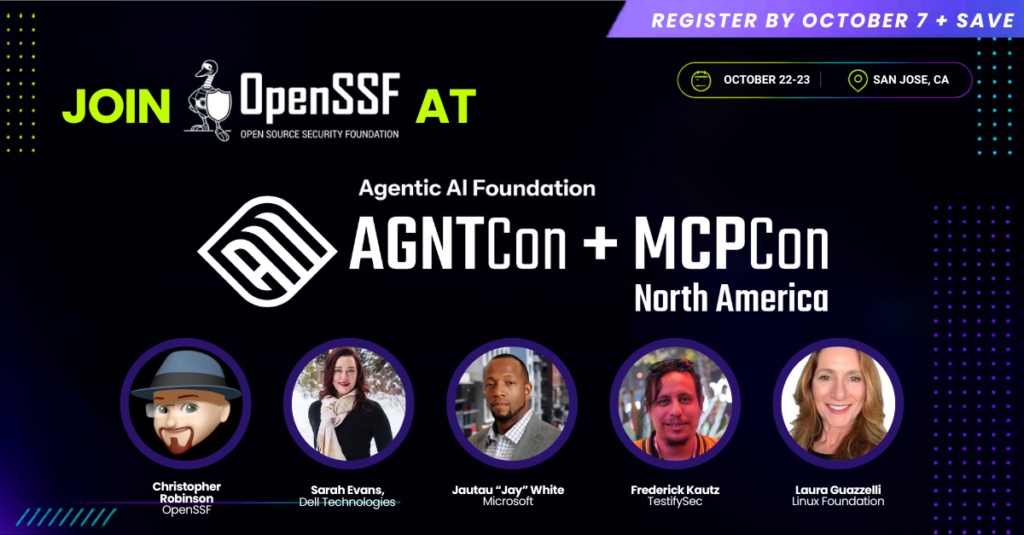 The OpenSSF is a proud Silver Sponsor at AGNTCon + MCPCon North America, happening October 22 and 23, 2026, in San Jose, CA. Securing agentic AI is the defining challenge of the year, and our community experts will be on the ground hosting deep-dive workshops and talks, including hands-on sessions covering the Secure Agentic Framework (SAF) and software supply chain defense.
Learn more | View the event schedule | Register today
Introducing BOMHort: Kubernetes-Native SBOM Visualization & Governance at Scale Joins the OpenSSF Sandbox
 We are excited to announce that BOMHort (formerly SeeBOM) has officially joined the OpenSSF family as a Sandbox Project! Authored by Mario Fahlandt, BOMHort is a Kubernetes-native platform designed to solve this exact challenge by delivering centralized visibility and governance for your software supply chain at scale. Read the full announcement
Case Study: Conquering the EU Cyber Resilience Act (CRA) with 1,400 Upstream Security Fixes
 Ericsson Software Technology met the CRA’s stringent obligations by fundamentally shifting to upstream collaboration. Guided by OpenSSF principles, the team eliminated private forks and contributed more than 1,400 dependency updates and security fixes directly back to open source communities. Read the case study
CRA Readiness: A Practitioner’s Guide to Compliance
 With the September 2026 reporting deadline approaching and full compliance required by December 2027, this Tech Talk lays out a clear, pragmatic path forward for software manufacturers, commercial entities, open source stewards, and foundations moving from policy interpretation to operational execution. Watch the recording, and stay tuned for the Tech Talk recap!
Announcing OpenBao v2.6!
 OpenBao v2.6 is here, adding per-namespace sealing and a new workflow engine for cross-plugin communication. Our most collaborative release to date, v2.6 features contributions from 42 first-time contributors, 27 individuals contributing multiple changes, and 8 users with double-digit change counts. Read the announcement
What’s in the SOSS? An OpenSSF Podcast
#67 – S3E19 Funding the Future: Community Collaboration and the Spirit of Open Source with Mila Zhou
Host Yesenia sits down with Mila Zhou, Open Source Program Manager at AWS, to explore the intersection of finance, strategy, and security in open source. Listen now
#68 – S3E20 CRA Readiness: Practical Strategies for Open Source Communities with Megan Knight
Megan Knight reviews the compliance timeline for the EU Cyber Resilience Act (CRA) and shares practical strategies for open source maintainers and shares key resources to help lower the barriers. Listen now
#69 – S3E21 Watering the Community Garden: Navigating the EU CRA for Open Source with Roman Zhukov
Roman Zhukov breaks down the EU Cyber Resilience Act (CRA) using a “community garden” analogy, comparing exempt open source maintainers to hobbyist gardeners, stewards to garden associations, and manufacturers to farm-to-table restaurants. Listen now
#70 – S3E22 Private Forks, CRA Deadlines, and the True Cost of Open Source Compliance with Dave Russo
Dave Russo breaks down the hidden $250,000-per-release financial toll of maintaining private forks, the crucial legal distinction between software manufacturers and open source stewards, and Red Hat’s framework for “champion stewardship.” Listen now
News from OpenSSF Community Meetings and Projects:
- The Global Cyber Policy Working Group launched a CRA Podcast Series focusing on practical readiness strategies for open source communities. The group is also collecting feedback for the new Cloud and AI Development Act to provide to the European Commission.
- In the CRA Tech Talk hosted by the Global Cyber Policy Working Group, leaders from the Orbit Launchpad Special Interest Group present their progress in building a machine-readable due diligence framework for open source software consumption. They discuss how tools like the CRAB-FOSS catalog and Dell’s Trustworthiness Calculator help manufacturers meet upcoming EU Cyber Resilience Act (CRA) compliance obligations. Watch the recording.
- The Vulnerability Disclosures WG published the OSS Vulnerability Guide documents as a new website: oss-vulnerability-guide.openssf.org
- The ORBIT Working Group announced that the Privateer sandbox application was approved by the TAC, beginning its formal donation process.
- The Secure Agentic Framework (SAF) SIG is actively planning a hands-on workshop for defenders of agentic AI at the upcoming AgentCon + MCPCon North America in San Jose.
- The Best Practices Working Group is progressing on its Secure Coding Guide for Python, focusing on rules backed by real-world CWEs and CVEs.
- OpenBao released v2.6.2, which includes security fixes for inline authentication workflows and PKI IP SAN enforcement alongside multiple bug fixes.
- Gemara released v1.5.0, introducing evidence mapping support to Evidence and AssessmentPlan structures.
- Minder released v0.3.1 to resolve server-side security vulnerabilities and expose rule evaluation outputs to Starlark tests.
- Zarf released v0.83.0, adding project vulnerability scanning with VEX statement support, improved pod security defaults, and an option to skip values schema validation.
- OSV Schema released v1.9.0, introducing support for the Homebrew and WordPress ecosystems along with wildcard package name support.
- Sigstore released Cosign v3.1.3 and backported v2.6.5 to fix a verification bypass vulnerability in legacy bundles.
- darnit announced its initial v0.1.0 release, providing security tooling integrations for MCP, PyPI, and container environments.
Cybersecurity Policy & Regulatory Updates:
- The CRA’s September 11, 2026 reporting deadline is fast approaching. As of that date, manufacturers and open source stewards must report actively exploited vulnerabilities and severe incidents through ENISA’s Single Reporting Platform (SRP).
- In preparation to the entry into application of the CRA reporting obligations on 11 September 2026, ENISA has updated its FAQs on the CRA SRP, and published additional set of very useful resources:
- A two-page factsheet on reporting;
- User guidance on how to register on the CRA SRP;
- User guidance on how to submit a notification.
- BSI (The German Federal Office for Information Security) has updated its TR-03183-1: Cyber Resilience Requirements – Part 1: General Requirements, a useful document that clarifies several aspects of the Cyber Resilience Act (CRA) and provides practical guidance on cyber resilience requirements; it forms part of BSI’s broader TR-03183 series on Cyber Resilience Requirements for manufacturers and products.
- CISA, together with a broad group of international cybersecurity agencies, has released the 2026 Minimum Elements for a Software Bill of Materials (SBOM).
- ETSI launches approval process for 17 EU CRA Vertical Standards.
- 593 amendments submitted for the revised Cybersecurity Act by The European Parliament committee on the Internal Market and Consumer Protection (IMCO) (amendments from 1 to 300, amendments from 301 to 593). For the revision of the NIS2 directive, belonging to the same cybersecurity package proposed at the beginning of this year, IMCO has submitted 91 amendments.
Meet OpenSSF at These Upcoming Events!
- OpenSSF Community Day Europe 2026 – October 6, Prague, Czechia
- Open Source Summit Europe 2026 – October 7–9, Prague, Czechia
- All Things Open 2026 – October 19–20, Edinburgh, UK
- ETSI Security Conference 2026 – October 19-22, Sophia Antipolis, France
- AGNTCon + MCPCon North America – October 20–23, San Jose, CA
- Open Source SecurityCon North America 2026 – November 9, Salt Lake City, UT
- KubeCon + CloudNativeCon North America 2026 – November 9–12, Salt Lake City, UT
Ways to Participate:
There are a number of ways for individuals and organizations to participate in OpenSSF. Learn more here.
You’re invited to…
- Join a Working Group or Project
- Chat with us on Slack
- Follow us on X, Mastodon, Bluesky, and LinkedIn
- Join OpenSSF
See You Next Month!
We want to get you the information you most want to see in your inbox. Missed our previous newsletters? Read here!
Have ideas or suggestions for next month’s newsletter about the OpenSSF? Let us know at marketing@openssf.org, and see you next month!
Regards,
The OpenSSF Team