
October brought four new members and fresh CRA resources from Prague, a practical guide to finding and fixing vulnerabilities with AI, and a new Sandbox project. Next stop: Salt Lake…
Read More
September brings a commitment to sustainable package registries, practical Cyber Resilience Act (CRA) guidance, new community security work, and three conversations on AI, regulation, and dependency risk. Join us in Prague for OpenSSF Community Day Europe on October 6.
5 min read
 Public package registries face rising security and operating costs. OpenSSF’s Governing Board commits to supporting sustainable funding models as enterprise customers while keeping access available to individual developers. Read the commitment.
IBM Enterprise Security Executive Jamie Thomas discusses how IBM’s historical journey with Java, Linux, and Red Hat shaped its strategy for turning open source software consumption into intentional stewardship, enterprise value, and career growth for developers. Through OpenSSF, that participation brings enterprise experience into a community working to secure the software upon which everyone depends. Learn more.
 OpenSSF and CNCF TAG Security are partnering on the fall Security Slam around KubeCon + CloudNativeCon North America. Learn how projects and contributors can take part.
 Meet emerging developers contributing to stronger software supply chain security through OpenSSF’s summer mentorship program. Read their stories.
 OpenSSF’s community garden journey helps maintainers, open source software stewards, and manufacturers identify the CRA guidance and resources relevant to their roles. Explore the journey and the community guide to the September 11 manufacturer reporting deadline.
 AWS describes how funding and scalable compute can support maintainers’ CI, fuzzing, testing, and artifact distribution. Read the guest blog.
 Discover key insights into the European Union Cyber Resilience Act (CRA) September 11, 2026 reporting obligations for manufacturers, alongside practical guidance enabling open source maintainers and stewards to streamline security response workflows. Read the community guide.
 The Government Digital Service (GDS) issued guidance reaffirming that public sector code should remain “open by default,” refuting NHS England’s decision to hide GitHub repositories over AI-driven vulnerability concerns by clarifying that opacity is not a valid substitute for proper security hygiene and rapid patching. Read here
#71 – S3E23 Navigating the New Era: The EU Cyber Resilience Act Explained with Madalin Neag
OpenSSF EU Policy Advisor Madalin Neag demystifies the EU Cyber Resilience Act (CRA). Learn how the CRA establishes a horizontal cybersecurity baseline for digital products. Listen now
Join Azure CTO and OpenSSF Board Chair Mark Russinovich as he discusses AI’s impact on software engineering, supply chain security, and vulnerability management. Listen now
In this episode of What’s in the SOSS, ActiveState CEO Abby Kearns breaks down the rapidly evolving open source security landscape. Listen now
There are a number of ways for individuals and organizations to participate in OpenSSF. Learn more here.
You’re invited to…
Join a Working Group or Project
Chat with us on Slack
Follow us on X, Mastodon, Bluesky, and LinkedIn
Missed an issue? Browse the newsletter archive. Send ideas for next month to marketing@openssf.org.
Regards,
The OpenSSF Team

🇳🇱 Open Source SecurityCon Europe → Agenda live and registration open
🎙️ Securing Agentic AI in Practice → March 17 Tech Talk on AI/ML security in action
📖 Compiler Annotations Guide → Practical C/C++ hardening without rewrites
🏆 Security Slam 2026 → 30-day challenge to level up project security
🇪🇺 CRA in Practice @ FOSDEM → Turning regulation into actionable steps
📦 Package Repository Security Forum → Cross-ecosystem collaboration in action
🎙️ What’s in the SOSS? → CFP tips and a 4-part AIxCC deep dive
6 min read
 Planning to attend KubeCon + Cloud Native Con Europe in March? Don’t miss OpenSSF’s co-located 1-day event! This gathering will bring together a diverse community, including software developers, security engineers, public sector experts, CISOs, CIOs, and tech pioneers, to explore challenges and opportunities in modern security. Collaborate with peers and discover the essential tools, knowledge, and strategies needed to ensure a safer, more secure future.
The agenda is live! Read the blog to learn what not to miss in Amsterdam and to see highlights from SecurityCon North America.
Read the blog | Register now | View the agenda
 Join us for the first OpenSSF Tech Talk of the year, focusing on agentic artificial intelligence (AI) security.
In this session, we will explore how the OpenSSF AI/ML Security Working Group is developing open guidance and frameworks to help secure AI and machine learning systems, and how that work translates into real-world practice. Using SAFE MCP and other solutions from OpenSSF member companies as examples, we will highlight community-driven efforts to improve the security of agentic AI systems, the problems they address, the design tradeoffs involved, and the lessons learned so far.
We will also feature OpenSSF’s free course, Secure AI/ML Driven Software Development (LFEL1012), which gives attendees a clear path to build practical skills and contribute to this rapidly evolving field.
Register and mark your calendar for March 17 at 1:00 p.m. ET. Additional speaker information will be shared soon.
 OpenSSF has released a new Compiler Annotations Guide for C and C++ to help developers improve memory safety, diagnostics, and overall software security by using compiler-supported annotations. The guide explains how annotations in GCC and Clang/LLVM can make code intent explicit, strengthen static analysis, reduce false positives, and enable more effective compile-time and run-time protections. As memory-safety issues continue to drive a significant share of vulnerabilities in C and C++ systems, the guide offers practical, real-world guidance for applying low-friction hardening techniques that improve security without requiring large-scale rewrites of existing codebases.
 Security Slam 2026 is a 30-day security hygiene challenge running from February 20 to March 20, culminating in an awards ceremony at KubeCon + CloudNativeCon Europe. Hosted by OpenSSF in partnership with CNCF TAG Security & Compliance and Sonatype, the event encourages projects to use practical security tools, including OpenSSF resources, to strengthen their security posture based on their maturity level. Participants can earn recognition, badges, and plaques for completing milestones, reinforcing a community-driven effort to improve open source software security at scale.
Read the blog to learn more | Register now to receive reminders and instructions
 At FOSDEM 2026, the CRA in Practice DevRoom brought together open source and industry leaders to turn the EU Cyber Resilience Act from policy discussion into practical action. Through case studies and panels, speakers shared concrete approaches to vulnerability management, SBOMs, VEX, risk assessment, and the steward role.
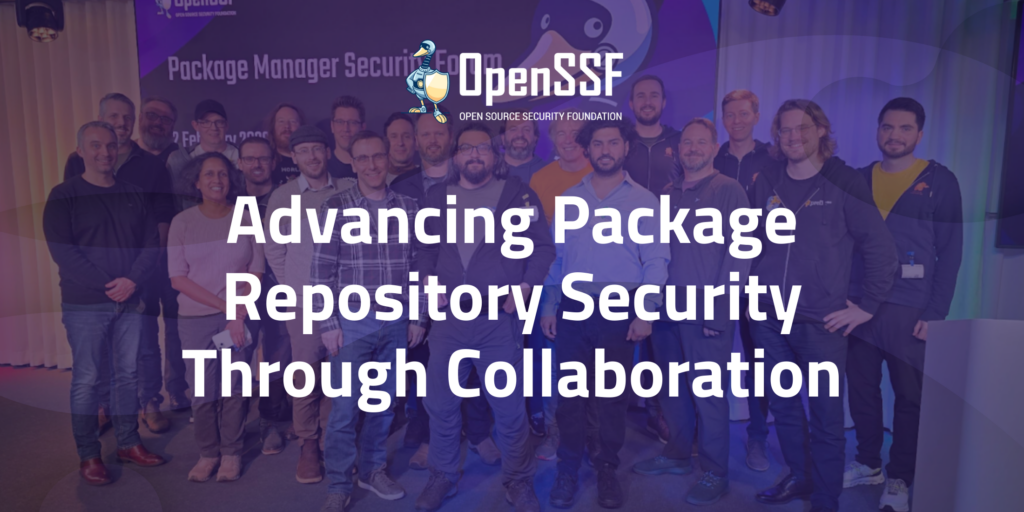 On February 2, OpenSSF convened the Package Manager Security Forum, bringing together maintainers and registry operators from major ecosystems to address shared challenges in package repository security. Discussions highlighted common concerns around identity and account security, governance and abuse handling, transparency, and long-term sustainability. The session reinforced that package ecosystem risks are interconnected and that improving security requires cross-ecosystem coordination, shared frameworks, and continued collaboration through OpenSSF’s neutral convening role.
 Is your open source project meeting the “minimum definition” of security? The OpenSSF has officially integrated the Open Source Project Security Baseline (OSPS Baseline) into its Best Practices Badge Program.
In our latest blog, David A. Wheeler explains how you can quickly identify and meet essential security requirements to earn a Baseline Badge.
#50 – S3E2 Demystifying the CFP Process with KubeCon North America Keynote Speakers
Stacey Potter and Adolfo “Puerco” García Veytia share practical, behind-the-scenes advice on submitting conference talks, fresh off their KubeCon keynote. They break down how CFP review committees work, what makes an abstract stand out, common mistakes to avoid, and why authenticity matters more than polish. The episode also tackles imposter syndrome and encourages new and diverse voices to shape the future of open source through speaking.
#51 – S3E3 AIxCC Part 1: From Skepticism to Success with Andrew Carney
Andrew Carney from DARPA explains the vision and results behind the two-year AI Cyber Challenge (AIxCC), which tasked teams with building AI systems that can automatically find and patch vulnerabilities in open source software. Despite early skepticism, competitors identified more than 80% of seeded vulnerabilities and generated effective patches at surprisingly low compute costs. The episode looks at what comes next as these cyber reasoning systems move from competition to real-world adoption.
#52 – S3E4 AIxCC Part 2: How Team Atlanta Won by Blending Traditional Security and LLMs
Professor Taesoo Kim of Georgia Tech describes how Team Atlanta combined fuzzing, symbolic execution, and large language models to win AIxCC. Initially skeptical of AI, the team shifted its strategy mid-competition and discovered that hybrid approaches produced the strongest results. The conversation also covers commercialization efforts, integration with OSS-Fuzz, and how the experience reshaped academic security research.
#53 – S3E5 AIxCC Part 3: Trail of Bits’ Hybrid Approach with Buttercup
Michael Brown of Trail of Bits discusses Buttercup, the second-place AIxCC system that pairs large language models with conventional software analysis tools. The team focused on using AI for well-scoped tasks like patch generation while relying on fuzzers for proof-of-vulnerability. Now fully open source and able to run on a laptop, Buttercup is actively maintained and positioned for broader enterprise and community use.
#54 – S3E6 AIxCC Part 4: Cyber Reasoning Systems in the Real World
CRob and Jeff Diecks wrap up the AIxCC series by exploring how competition teams are applying their systems to real open source projects such as the Linux kernel and CUPS. They introduce the OSS-CRS initiative, which aims to standardize and combine components from multiple cyber reasoning systems, and share lessons learned about responsibly reporting AI-generated findings. The episode highlights how collaboration through OpenSSF’s AI/ML Security Working Group and Cyber Reasoning Systems SIG is shaping the next phase of AI-driven security.
Connect with the OpenSSF Community at these key events:
Ways to Participate:
There are a number of ways for individuals and organizations to participate in OpenSSF. Learn more here.
You’re invited to…
We want to get you the information you most want to see in your inbox. Missed our previous newsletters? Read here!
Have ideas or suggestions for next month’s newsletter about the OpenSSF? Let us know at marketing@openssf.org, and see you next month!
Regards,
The OpenSSF Team
Welcome to the January 2026 edition of the OpenSSF Newsletter. This issue highlights new research, community priorities, and upcoming events across the open source security ecosystem.
📊 2026 Cyber Resiliency Survey → Measure the awareness of CRA
🧭 OpenSSF 2026 Themes → What’s ahead and how to get involved
🔎 VEX, AI & OSPS Baseline → Practical blogs and podcast highlights
🌍 Events & Community → GVIP Summit, EU Policy Summit, FOSDEM, Open Source SecurityCon Europe, CFPs, and project updates
 As cybersecurity legislation such as the EU Cyber Resilience Act (CRA) takes effect, open source communities are beginning to feel its impact, from maintainers and contributors to organizations that rely on open source every day. Building on last year’s inaugural study, Linux Foundation Research and OpenSSF are again inviting the community to share perspectives through a new survey focused on awareness and readiness for cybersecurity regulation.
Your perspective matters. By participating, you help strengthen shared understanding, surface real community needs, and support the open source ecosystem as it navigates emerging regulatory challenges. Take the Survey.
OpenSSF is heading to Brussels for FOSDEM 2026 and Open Source Week, building on last year’s momentum around practical open source security, CRA readiness, and community-driven solutions. Expect strong presence across policy and technical devrooms, a joint booth with Linux Foundation Europe (K2-A-03), and active participation in key events like the GVIP Summit and EU Open Source Policy Summit. The focus this year: turning regulation and security best practices into real, usable tooling and guidance for maintainers and projects. Read the blog.
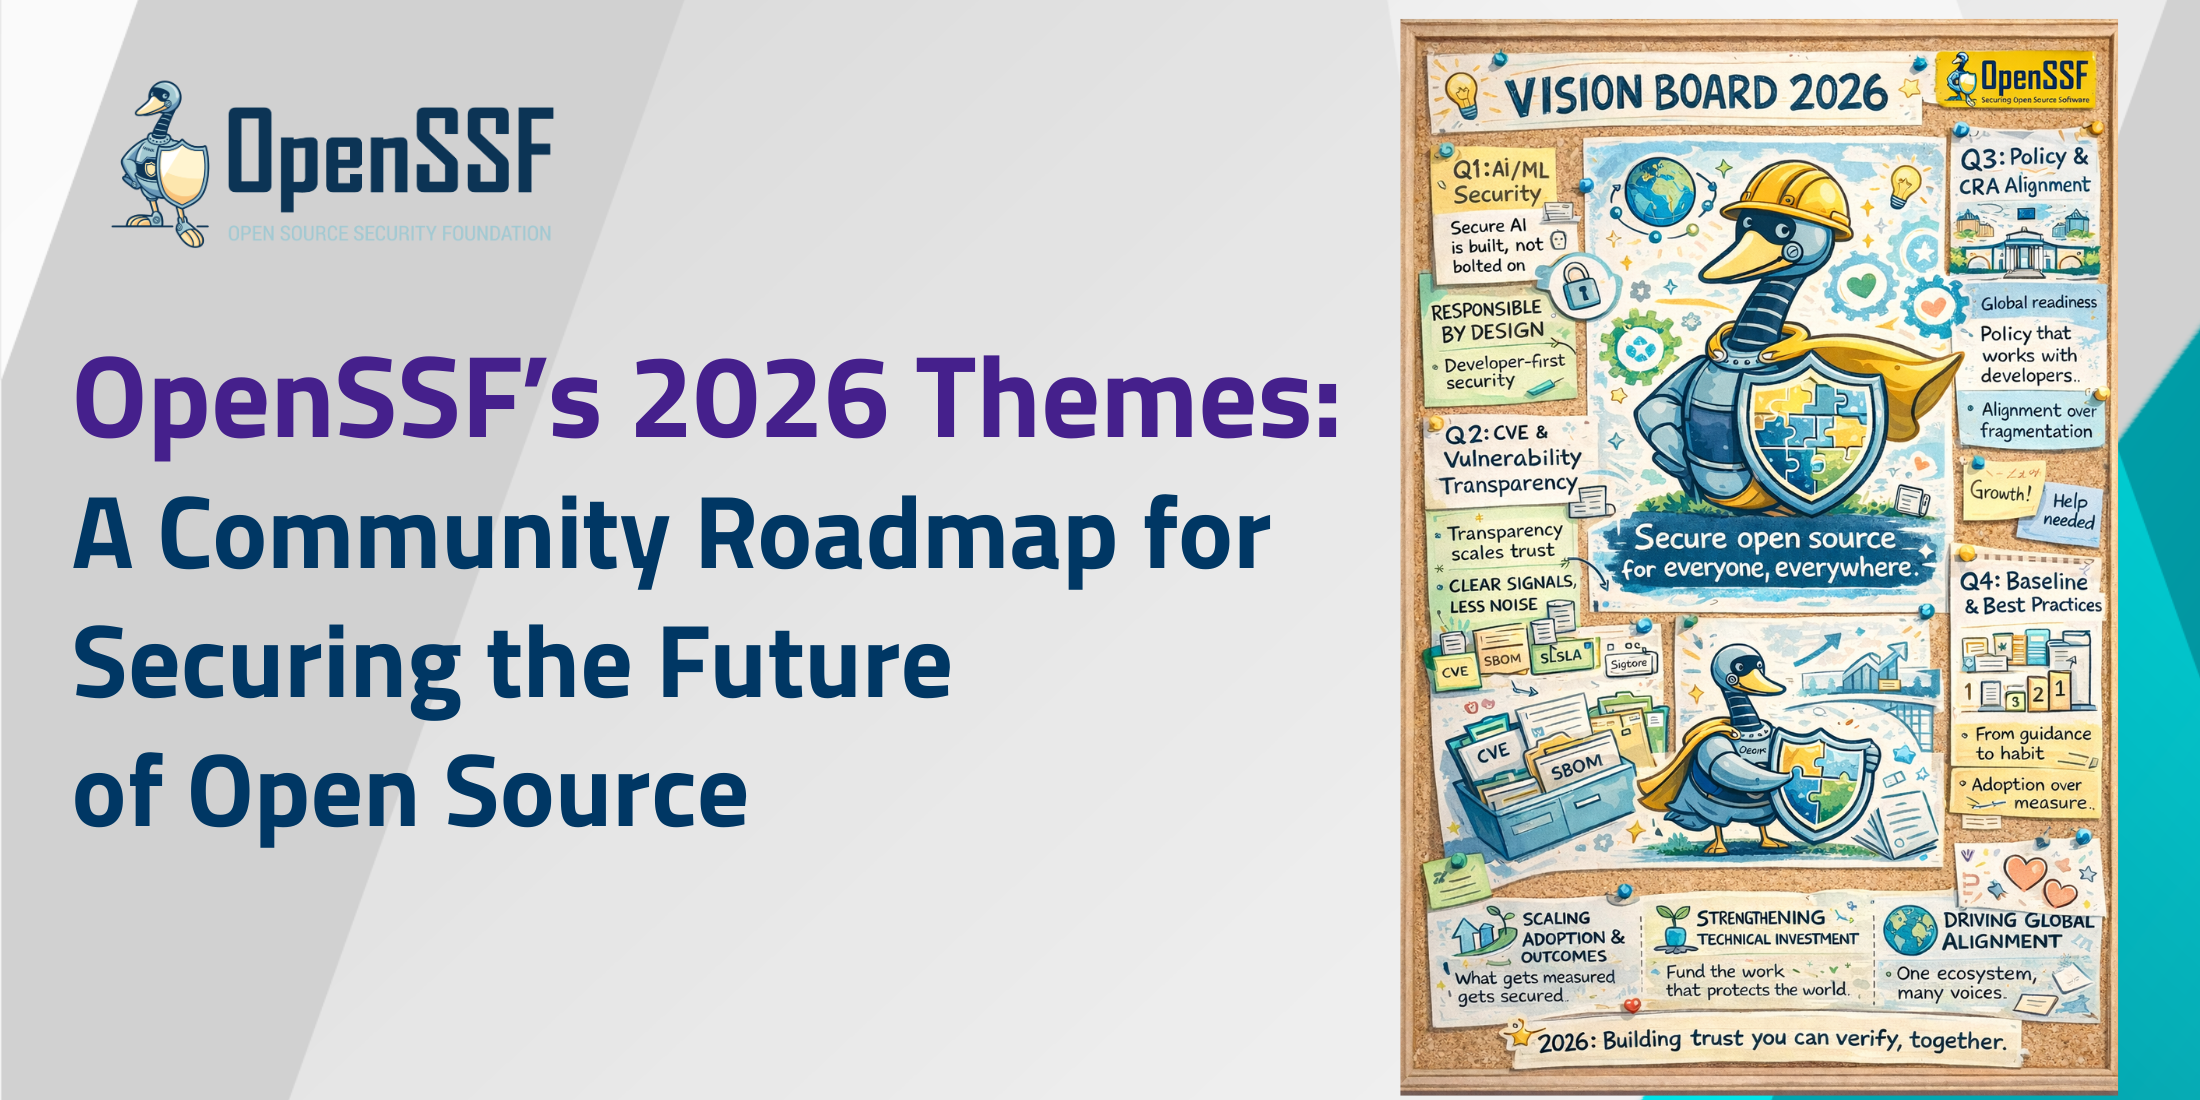 Curious about what security topics will shape the open source world in 2026 and how you can be part of it? Read about OpenSSF’s quarterly themes from AI and ML security to vulnerability transparency, global policy alignment, and Baseline adoption. This blog also highlights key events, community activities, and how to get involved. Read more.
Key stakeholders, Aubrey Olandt (Red Hat), Brandon Lum (Google), Charl de Nysschen (Google), Christoph Plutte (Ericsson), Georg Kunz (Ericsson), Jonathan Douglas (Microsoft), Jautau “Jay” White (Microsoft), Martin Prpič (Red Hat), and Rao Lakkakula (Microsoft) look at how VEX is developing across the software industry. VEX provides structured, machine-readable statements about whether a vulnerability affects a product. It can reduce false positives and cut down the workload for security teams, but adoption is still uneven. This report reviews the main VEX formats CSAF, OpenVEX, CycloneDX, and SPDX and highlights gaps in tooling, trust, and distribution. Read more.
In this guest blog from Trail of Bits, learn how transparency logs like Rekor, combined with tools such as rekor-monitor, help package maintainers spot tampering and unauthorized signatures in real time. With support from OpenSSF, new improvements make monitoring easier, more reliable, and ready for production, an important step toward securing the open source software supply chain.
Read the full blog to see how transparency logs work, why they matter, and what’s coming next.
How is AI really changing software development today? In “AI, Software Development, Security, Tips, and the Future (Part 1)”, David A. Wheeler notes that AI use during software development has become the norm because “productivity is king,” even though AI-generated results are frequently wrong, and discusses the security risks around development environments and insecure generated code. In Part 2, he continues by offering practical tips on how developers can better use AI, touches on licensing and “vibe coding,” and looks toward the future, explaining that AI won’t replace developers anytime soon, but will increase both attack and defense capabilities in software security. If you haven’t read both blogs yet, they provide a clear, realistic view of how AI is affecting software today and what developers should be thinking about next.
 What does good security actually look like for open source projects? This new blog walks through the community-developed OSPS Baseline, a catalog of practical security controls that helps projects understand expectations, improve over time, and meet users where they are. With FOSS in up to 96% of modern codebases and relied on across nearly every industry, the blog explains why shared security practices matter and how the Baseline connects to standards like NIST SSDF, the EU Cyber Resilience Act, and ISO 27001. It also links to keynotes, a tech talk, a podcast, a real project case study, and FAQs so you can see how the Baseline works in practice. Read the blog.
How does it feel to represent a global open source security community across Europe? In his blog, Madalin Neag reflects on attending key open source, cybersecurity, and standardization meetings on behalf of OpenSSF throughout 2025. He describes how each conference badge represents conversations, collaboration, and the growing understanding that open source security is becoming an essential part of Europe’s cybersecurity future. The blog highlights the connections formed between maintainers, policymakers, standards groups, and community leaders, and shows how work in open source security bridges policy and practice across many different environments. Read more.
This blog looks at how voluntary security attestation models under the EU Cyber Resilience Act could unintentionally shift risk and responsibility onto open source developers. It argues that CRA compliance should stay focused on downstream manufacturers and rely on automation and verifiable security metadata rather than upstream attestations that could undermine open source sustainability.
#47 – S2E24 Teaching the Next Generation: Software Supply Chain Security in Academia with Justin Cappos
This episode goes inside academia with NYU’s Justin Cappos, who explains why universities struggle to teach software supply chain security and how his course is producing highly skilled professionals. He and Yesenia Yser talk about curriculum, real-world open source collaboration, and how the Linux Foundation’s Academic Computing Acceleration Program could reshape security education.
#48 – S2E25 2025 Year End Wrap Up: Celebrating 5 Years of Open Source Security Impact!
CRob and Yesenia close out the year with a special wrap-up celebrating OpenSSF’s fifth anniversary and a huge year in open source security. They look back at new free training courses, highlights from the DARPA AI Cyber Challenge, standout interviews, major projects such as, OSPS Baseline and AI model signing, and community conversations across SBOMs and supply chain security. With nearly 12,000 downloads and big plans for Season 3, this episode is a fun look at how far the community has come and what’s ahead in 2026.
#49 – S3E1 Why Marketing Matters in Open Source: Introducing Co-Host Sally Cooper
In this Season 3 premiere, What’s in the SOSS? welcomes Sally Cooper as an official co-host. Sally shares her path from technical training and documentation to marketing leadership at OpenSSF, and explains why marketing matters in open source communities. Joined by CRob and Yesenia Yser, the conversation explores personas, personal branding, trust, and how marketing helps great projects get discovered, supported, and sustained. The episode also offers a preview of OpenSSF’s 2026 marketing themes and practical ways for newcomers to get involved.
Connect with the OpenSSF Community at these key events:
There are a number of ways for individuals and organizations to participate in OpenSSF. Learn more here.
You’re invited to…
We want to get you the information you most want to see in your inbox. Missed our previous newsletters? Read here!
Have ideas or suggestions for next month’s newsletter about the OpenSSF? Let us know at marketing@openssf.org, and see you next month!
Regards,
The OpenSSF Team