
By Alex Scheel
Summary
Open Source Summit and its co-located events are always a great time to build bridges in the open source community, and OSS Europe 2026 and OpenSSF Community Day Europe were no exceptions. The newly inaugurated OpenSSF ambassadors, just announced at OSS NA 2026 back in May, were out in numbers: talks by Hannah Braswell, Roman Zhukov, and Yunseong Choi appeared at Tuesday’s Community Day while a talk by Kadi McKean and Katherine Druckman and two by Roman Zhukov were at the main conference. Many OpenSSF staff members, TAC representatives, and community members gave talks as well, including part two of the popular and hilarious Game Show by Christopher “CRob” Robinson and Adrianne Marcum from OpenSSF Community Day NA.
The OpenSSF booth saw a number of great discussions with everyone from visitors unfamiliar with OpenSSF to long-time community members. The OpenSSF CRAFish plushie and glow-in-the-dark OpenBao stickers were definitely fan favorite swag.
But the headline event was the keynote by Jamie Thomas talking about how the OpenSSF and newly launched Akrites are helping communities secure their software from the next generation of AI threats.
The Bridges of Prague
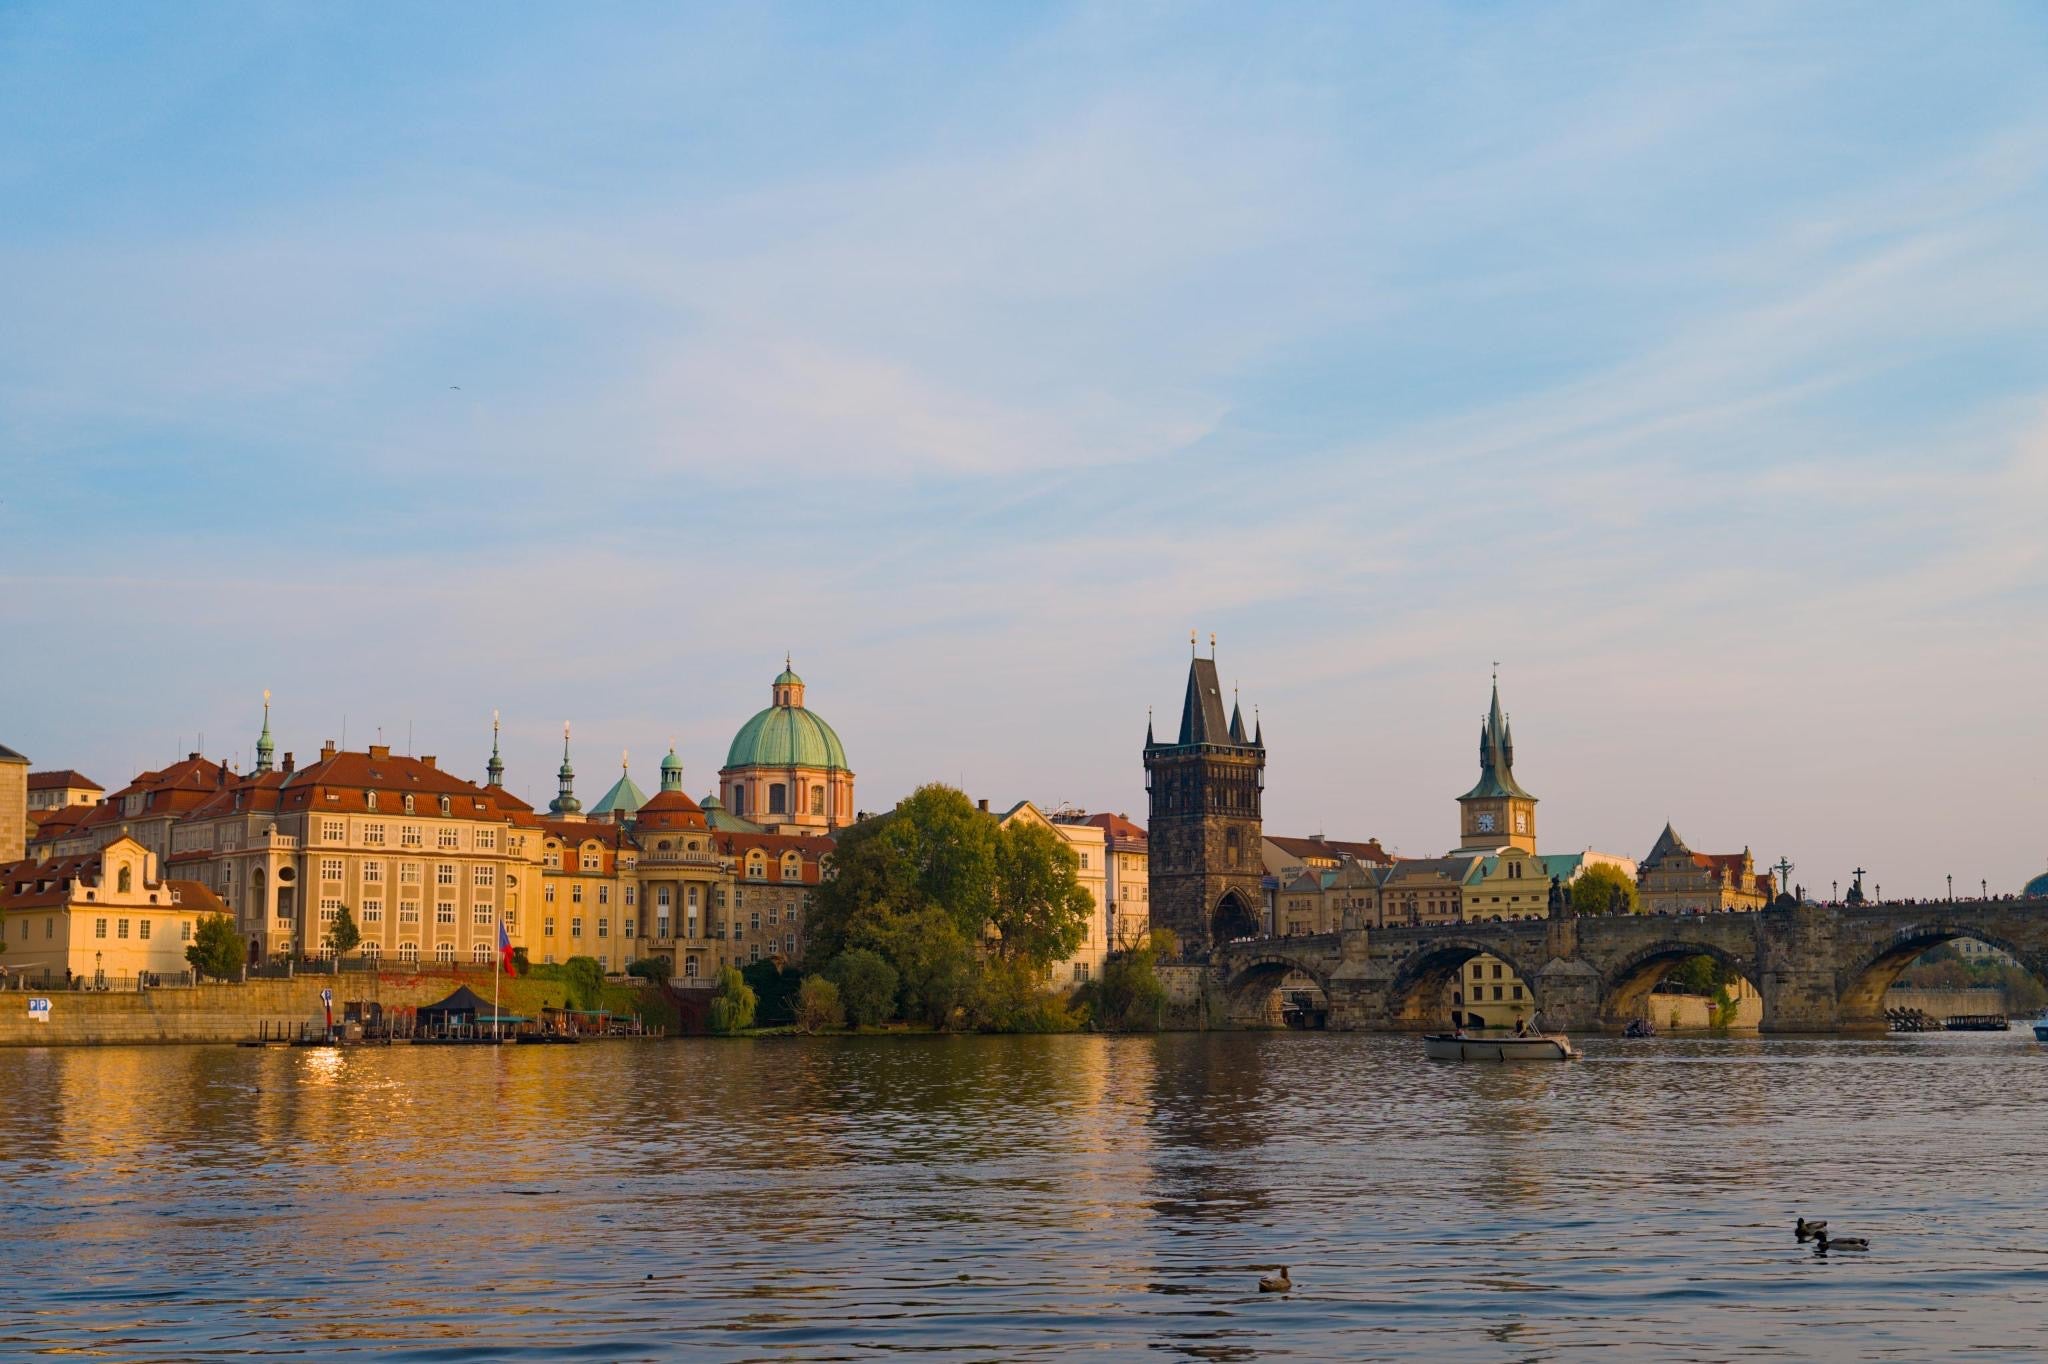
(Image courtesy of Katherine Mayo; used with permission.)
Prague is a city split across the two banks of the Vltava River and, like any such city, needs bridges to connect people living and working on opposite sides together. The oldest bridge still standing is the famous Charles Bridge, started in 1357 under King Charles IV, and is pictured above. It is currently a pedestrian bridge, however, and Prague also has many newer bridges, built as the needs and traffic patterns of the city have changed throughout time.
To me, and no doubt many others, OSS EU served as a bridge to catch up with OpenSSF and OpenBao community members. Many OpenBao community members were present–from ControlPlane and elsewhere–while other organizations that participate in the ecosystem–like SAP, Ericsson, Percona, Sylva, and the NeoNeophos foundation–had booths at the events. Pleasantly surprising were the number of OpenBao users we met with at the OpenSSF booth. From all industries–healthcare, energy, finance–and geographies–Europe, Asia, and the Americas–users came up to us and shared their stories of integrating OpenBao in their company or home lab. In this way, the bridge of OSS EU connected us to many exciting activities of our community members.
How Did Prague’s Landmark Bridges Mirror Our Community Connections?
Like the bridges of Prague, conversations often ran in many parallel directions. Where Jamie Thomas’s keynote addressed the surge in new vulnerability reports and how Akrites can facilitate that, discussions at the booth talked about identifying gaps through OSS-CRS, and a talk by Gabriel Columbro of FINOS and Francesco Beltramini of ControlPlane talked about how financial services institutions are tackling the patching problem with OSERA. This was reflected in the parallels between all manners of community members: maintainers were dealing with the influx of reports and the requirements of the EU’s Cyber Resilience Act, operators were trying to understand how to patch, and industry leaders were looking to understand the latest trends and their impact on their organizations.
In conjunction with Linux Foundation Research, the OpenSSF’s recently published 2026 CRA Readiness Report highlighted a reality felt by everyone: CVE discoveries surged 394% year-over-year in Q1 2026, with high-severity vulnerabilities up 811% across 14,000+ open source projects. The consensus was that this trend would continue and, if anything, accelerate.
Where is the OpenSSF going and where have we been?
At the main conference, Adrianne Marcum and CRob explored AI slop and emerging security challenges in AI Everywhere, Trust Nowhere. Madalin Neag joined Roman Zhukov, Daniel Appelquist, and Megan Knight for the October 9 Workshop on operationalizing the Cyber Resilience Act. Madalin also presented Open Source Security as the Foundation of European Sovereignty with Mirko Boehm and CRA Compliance Paths and Where the Real Responsibility Sits.
Also from OpenSSF members was a panel on SBOM quality with Takashi Ninjouji, Yoshiyuki Ito, Kiyoshi Owada, Tsukasa Yobo, and Yumi Tomita; exploring AI assisted CVE triage with Kazuyoshi Akiyama and Takashi Ninjouji, connecting regulatory intent and operational reality with ORBIT Launchpad by Rao Lakkakula and Sarah Evans; measuring the health of the NPM ecosystem from Adam Herzog and Alyssa Wright and many by non-members new to our community.
What is next for the OpenSSF community?
Check us out at SecurityCon during KubeCon North America on November 9th or at next year’s Open Source Summit North America in Vancouver, BC! You can look at other upcoming OpenSSF events and subscribe to the OpenSSF newsletter to stay up to date on the latest between conferences.
Missed a talk from Open Source Summit Europe 2026?
Check out the OpenSSF channel on YouTube for playlists on talks at the OpenSSF Community Day and Summit. The recordings are now available and you can watch all of the mentioned presentations.
About the Author
 Alex Scheel (“cipherboy”) is the Head of OpenBao Development at ControlPlane, a member of the OpenBao Technical Steering Committee, and Chair of the OpenBao Development Working Group. He has built a career on open source contributions, previously working at GitLab with OpenBao, at Keyfactor on Bouncy Castle, at HashiCorp on Vault, and at Canonical and Red Hat. He continues to participate in and give back to the Minnesota arts community and serves as a board member for the Artaria String Quartet.