Discover how the EU Cyber Resilience Act (CRA) impacts your open source work. OpenSSF’s new community garden user journey helps maintainers, software stewards, and manufacturers navigate legal requirements and find…
How can open source projects maintain secure infrastructure without financial strain? OpenSSF Premier Member, Amazon Web Services (AWS) addresses this by providing critical funding and scalable compute resources.
The EU Cyber Resilience Act is no longer a distant regulatory concept. With vulnerability reporting obligations to ENISA arriving on September 11 and the full weight of the law landing…
Join Azure CTO and OpenSSF Chair Mark Russinovich as he discusses AI's impact on software engineering, supply chain security, and vulnerability management.
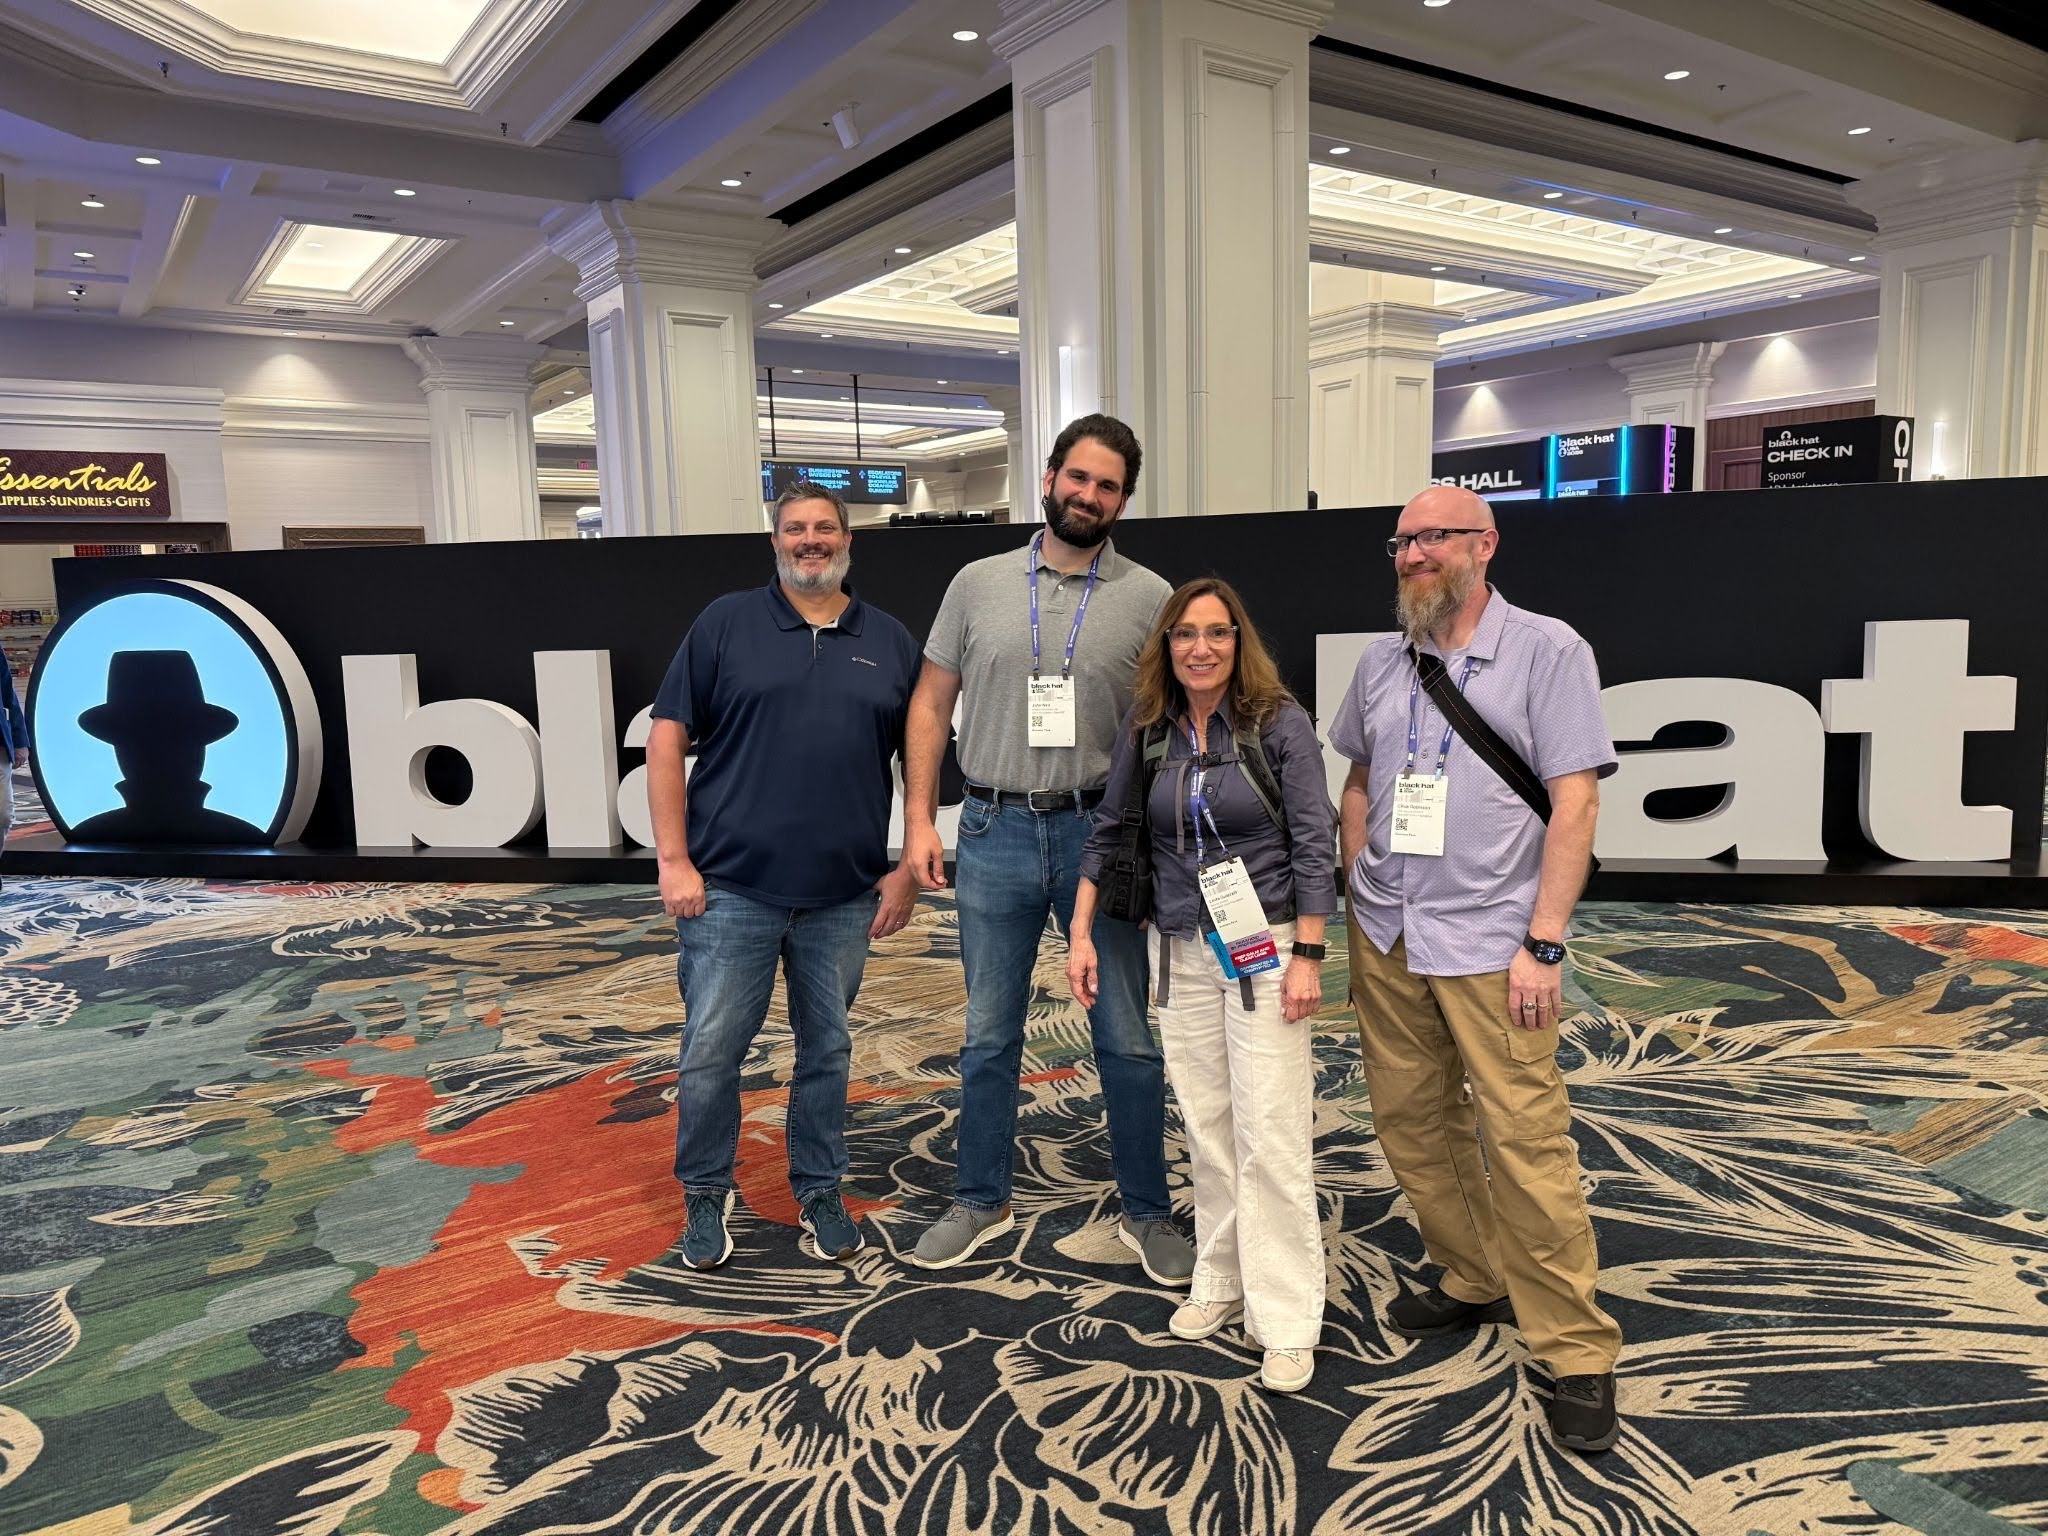
Las Vegas was once again the center of the cybersecurity universe from August 1–9 for Black Hat and DEF CON 2026. The Open Source Security Foundation (OpenSSF) had a major…
In this episode of What’s in the SOSS, host Sally Cooper and OpenSSF EU Policy Advisor Madalin Neag demystify the EU Cyber Resilience Act (CRA). Learn how the CRA establishes…
The August 2026 OpenSSF Newsletter spotlights a wave of CRA readiness content, from a new Ericsson case study to a four-part podcast run on compliance.
As regulatory requirements like the EU Cyber Resilience Act (CRA), NIST SSDF, and Executive Order 14028 take effect, generating a Software Bill of Materials (SBOM) has shifted from a best…
Join OpenSSF at AGNTCon + MCPCon North America this October to explore the Secure Agentic Framework (SAF) and learn how to secure the future of agentic AI ecosystems.
Ericsson Software Technology successfully met the stringent obligations of the EU Cyber Resilience Act (CRA) by fundamentally shifting to upstream collaboration. Guided by OpenSSF principles, they eliminated private forks and…