
OpenSSF
What’s in the SOSS? Podcast #72 – S3E24 Balancing AI’s Double-Edged Sword: Software Engineering, Unlearning, and Ecosystem Sustainability with Mark Russinovich
Join Azure CTO and OpenSSF Chair Mark Russinovich as he discusses AI's impact on software engineering, supply chain security, and vulnerability management.
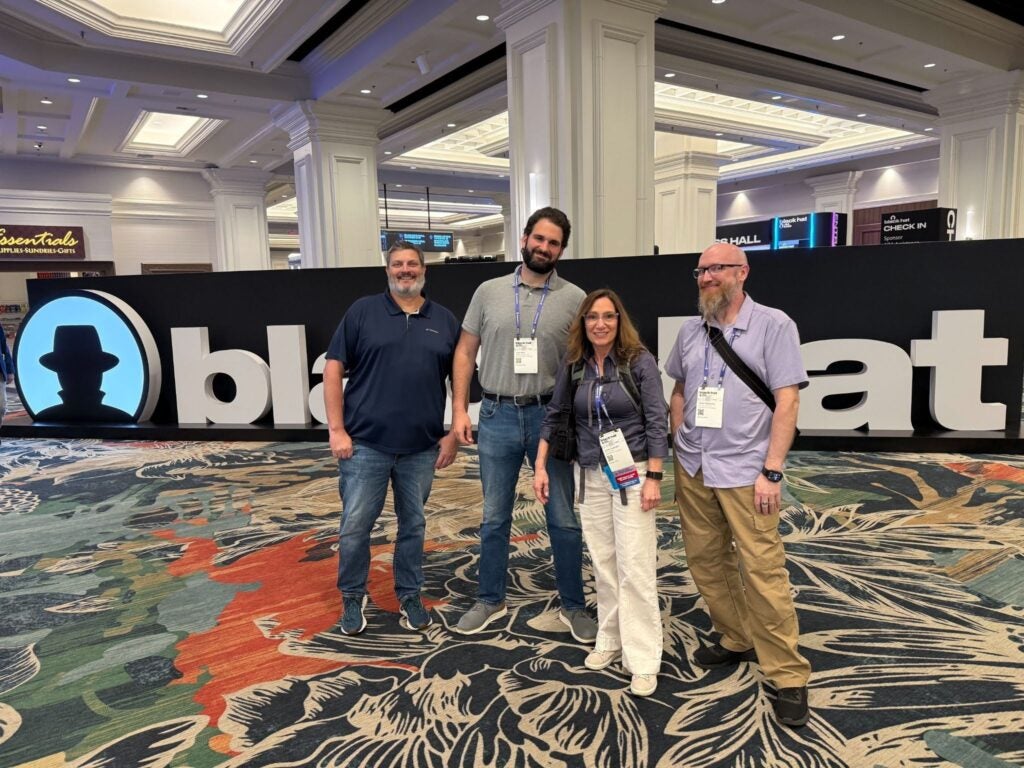
OpenSSF at Hacker Summer Camp 2026: Black Hat & DEF CON Highlights and Recap
Las Vegas was once again the center of the cybersecurity universe from August 1–9 for Black Hat and DEF CON 2026. The Open Source Security Foundation (OpenSSF) had a major presence throughout the week, engaging with security leaders, project maintainers, and the broader community to advance open source security.
What’s in the SOSS? Podcast #71 – S3E23 Navigating the New Era: The EU Cyber Resilience Act Explained with Madalin Neag
In this episode of What’s in the SOSS, host Sally Cooper and OpenSSF EU Policy Advisor Madalin Neag demystify the EU Cyber Resilience Act (CRA). Learn how the CRA establishes a new cybersecurity baseline and what it means for open source maintainers, contributors, and the global software supply chain.
OpenSSF Newsletter – August 2026
The August 2026 OpenSSF Newsletter spotlights a wave of CRA readiness content, from a new Ericsson case study to a four-part podcast run on compliance.
Introducing BOMHort: Kubernetes-Native SBOM Visualization & Governance at Scale Joins the OpenSSF Sandbox
As regulatory requirements like the EU Cyber Resilience Act (CRA), NIST SSDF, and Executive Order 14028 take effect, generating a Software Bill of Materials (SBOM) has shifted from a best practice to a strict requirement. However, for platform and security teams, generating SBOMs is only half the battle. Managing, querying, and analyzing thousands of SPDX…
Join OpenSSF at AGNTCon + MCPCon North America: Securing Agentic AI
Join OpenSSF at AGNTCon + MCPCon North America this October to explore the Secure Agentic Framework (SAF) and learn how to secure the future of agentic AI ecosystems.
Case Study: Conquering the EU Cyber Resilience Act (CRA) with 1,400 Upstream Security Fixes
Ericsson Software Technology successfully met the stringent obligations of the EU Cyber Resilience Act (CRA) by fundamentally shifting to upstream collaboration. Guided by OpenSSF principles, they eliminated private forks and contributed over 1,400 dependency updates and security fixes directly to open source communities.
What’s in the SOSS? Podcast #70 – S3E22 Private Forks, CRA Deadlines, and the True Cost of Open Source Compliance with Dave Russo
In this episode of What's in the SOSS, host Sally Cooper and Red Hat's Dave Russo unpack the European Union’s Cyber Resilience Act (CRA). Discover the hidden financial toll of private forks, the crucial legal distinction between manufacturers and open source stewards, and actionable steps your organization can take to meet upcoming compliance deadlines.