Artificial intelligence (AI) is changing how software is developed, maintained, and secured. In State of AI Impact on Software Security and Cybersecurity 2026, OpenSSF joins Linux Foundation Research, ActiveState, and LF AI & Data to explore how security practitioners across organizations and open source projects are responding to emerging risks and opportunities.
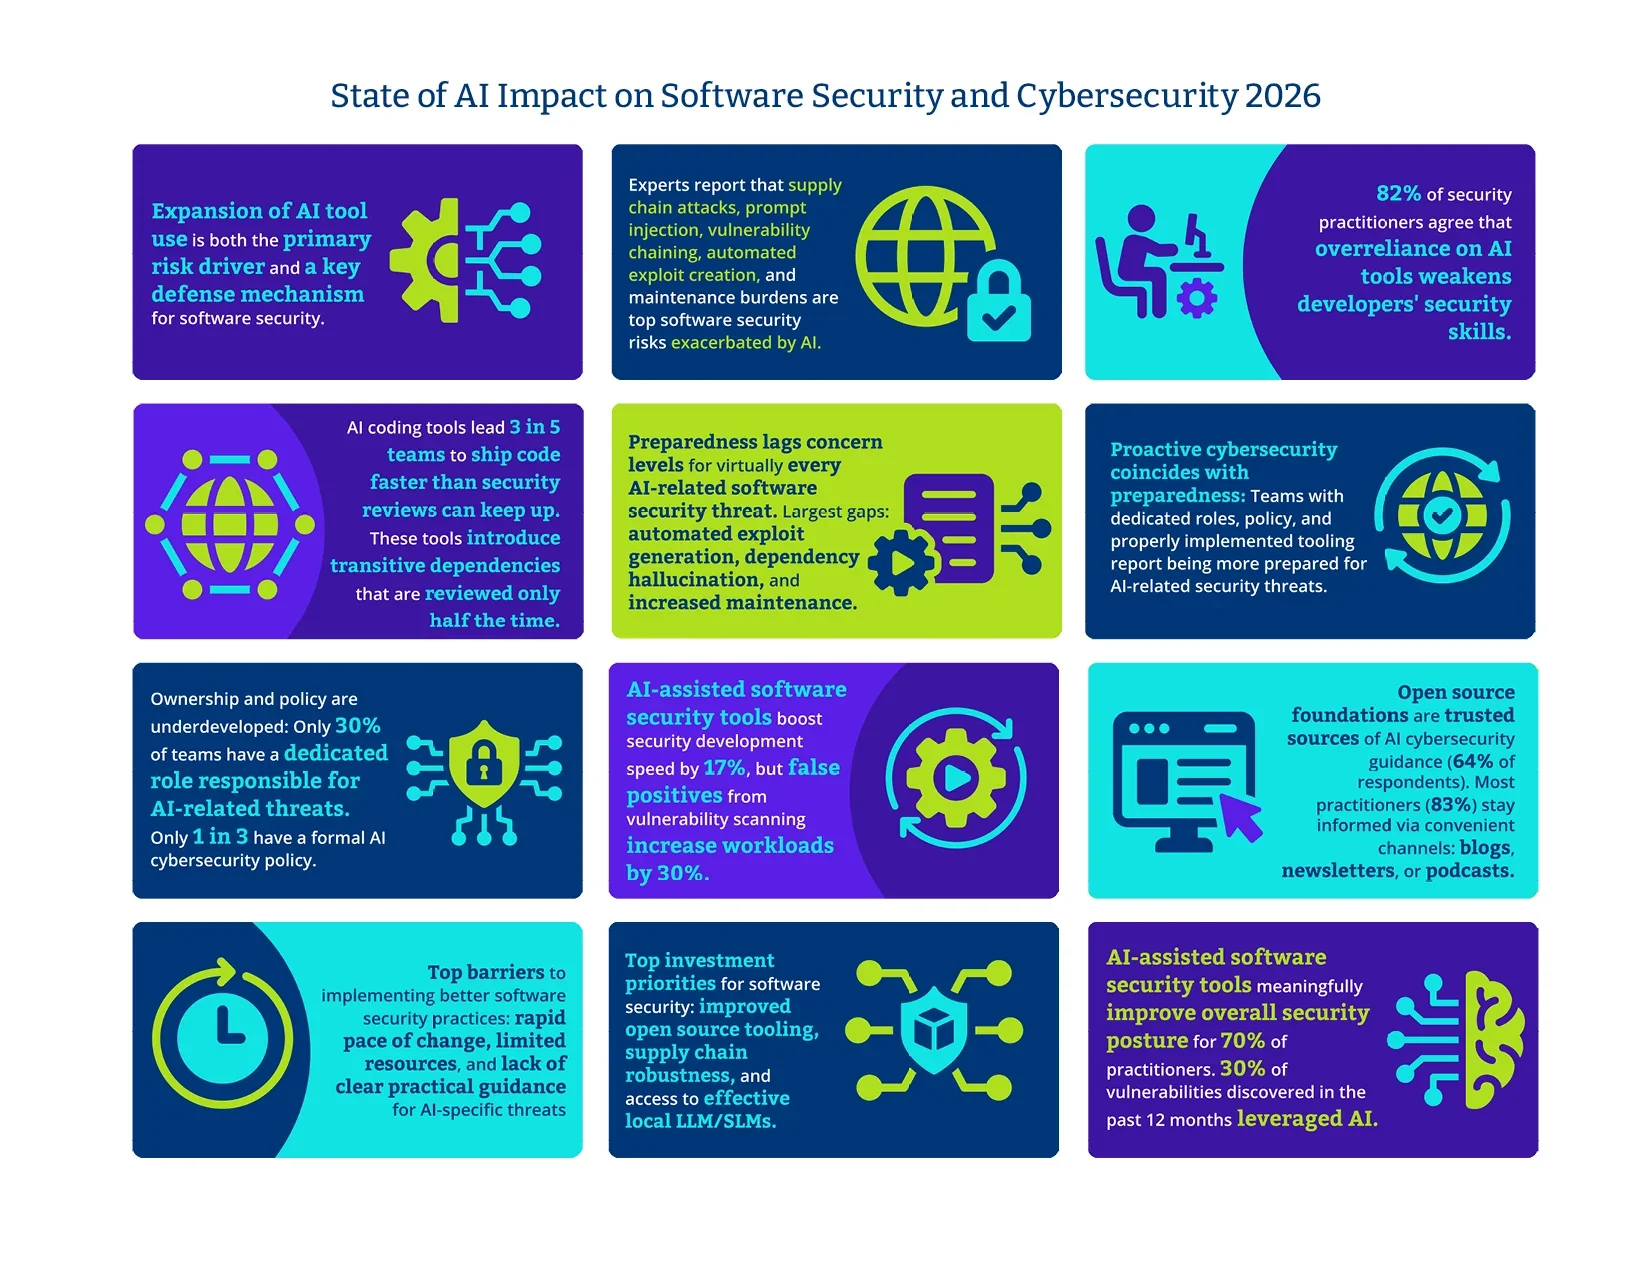
The findings reveal that 58% of respondents say their teams ship code faster than security review can keep up, while 60% say AI coding tools increase external dependencies. Only 30% of teams have a dedicated role responsible for AI-related security threats. Teams with dedicated roles or formal AI security policies report greater preparedness, highlighting the importance of clear ownership and governance.
As Laura Guazzelli, OpenSSF Security Architect AI / ML / LLM / Agentic Systems writes in the report’s foreword:
“Many projects can’t hire dedicated specialists. Shared open source tooling and practical guidance can close some of that gap. Investing in the communities that maintain our software is investing in our own security.”
The report explores how organizations and maintainers can strengthen dependency management, improve security review, and use AI-assisted tools responsibly to help keep open source software secure and sustainable.
Authors
- Sam Boysel, The Linux Foundation
- Foreword by Laura Guazzelli, OpenSSF
Sponsored By